
MetaMask Snap
Evidence before you confirm.
Proof Before Sign runs inside the MetaMask confirmation window. It traces the exact transaction you are about to sign, compares the live code with independently reviewed code, and shows who can still change it.
Using another wallet? Get the browser extension.
POA never needs your recovery phrase or private key. The proposed transaction is sent to POA for analysis; your wallet address and calldata are not stored.
Install · MetaMask Snap
MetaMask Flask
Checking…
Reading the live release configuration.
Release 0.11.0
Release pending
Built and verified, not on npm yet. Until it is published, MetaMask Flask keeps installing the version above.
This browser
Checking installation availability…
MetaMask reports Snaps connected to this website. Installation also reconnects an existing Snap.
New in 0.11.0Release pending
Audit evidence for each call, inside the confirmation
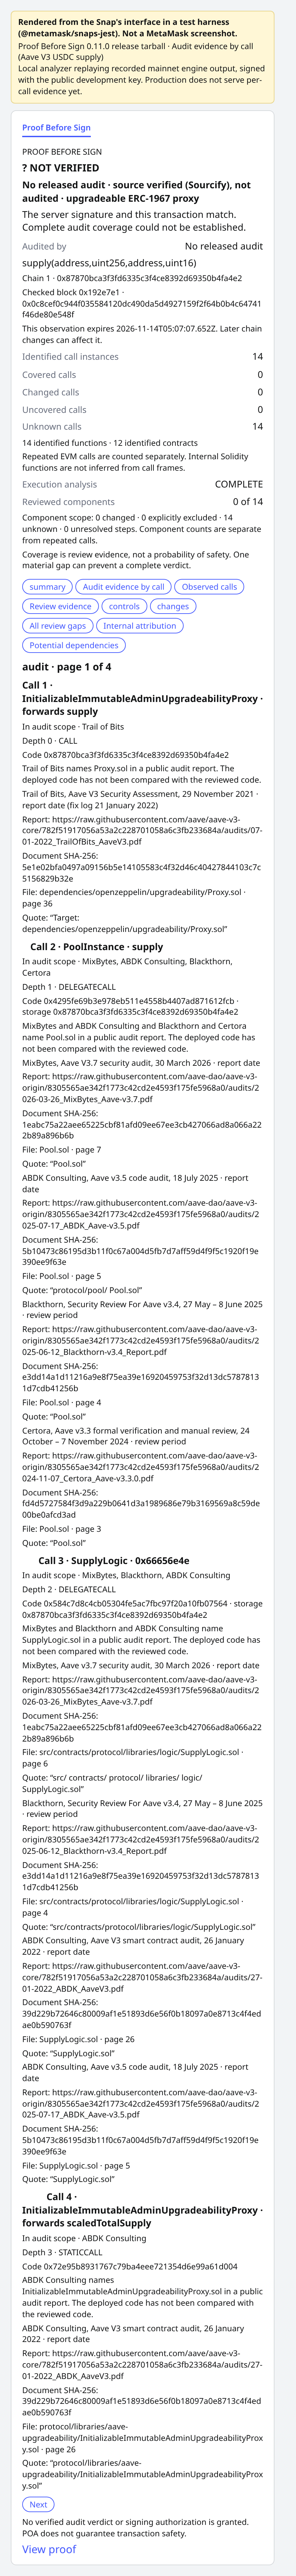
One transaction often runs several contracts. Version 0.11.0 adds a breakdown to the POA tab in MetaMask that lists each call and says which public audit reports name its code.
- Calls checked
- How many calls the transaction makes, counted from the traced execution.
- Each call, in order
- Every call in the order it runs, with its depth and call type, through proxies to the implementation that runs.
- Firms
- The audit firms whose public reports name the file, with the report, its SHA-256, the page and the quoted line.
- Status of each call
- Byte-for-byte matchDeployed code is the build of the reviewed commit.
- In audit scopeA public audit report names the file this code comes from.
- No audit foundThe report we hold for this protocol lists its files and does not name this one.
- Not checkedOur evidence cannot say either way.
The rows are evidence, not a release. They do not change the verdict at the top of the panel.
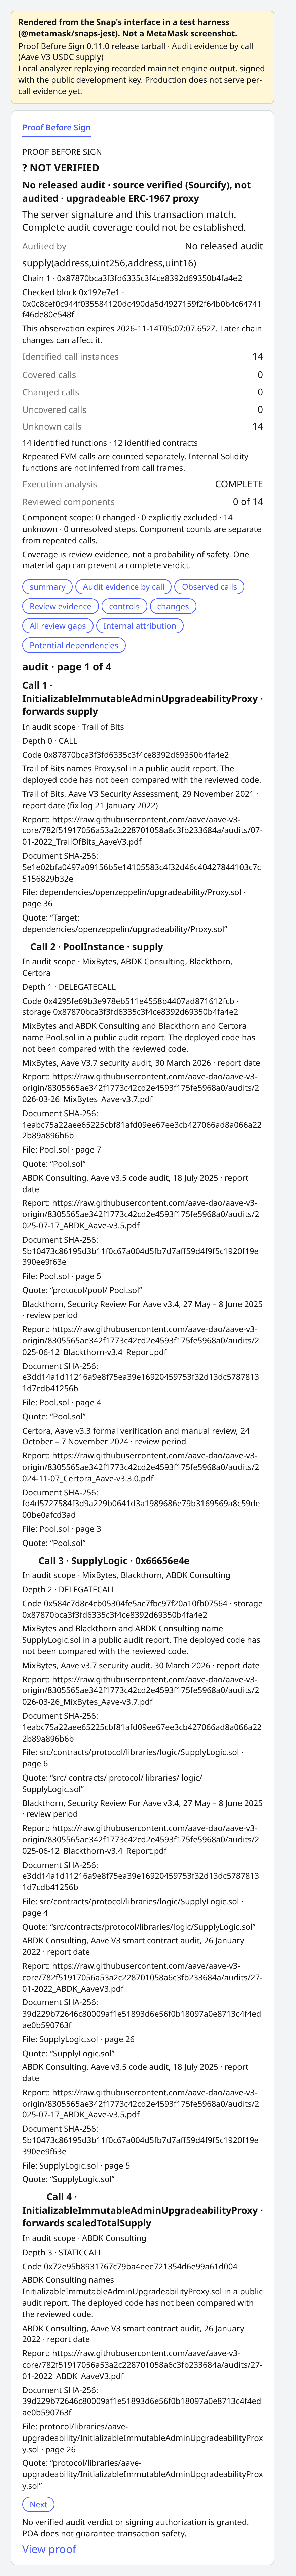
Rendered from the 0.11.0 release tarball by the Snap test harness (@metamask/snaps-jest), from recorded mainnet analyzer output. Not a MetaMask screenshot. Scroll inside the frame to read each call. Open full size
Other panels from the same build · Rendered from 0.11.0 by the test harness
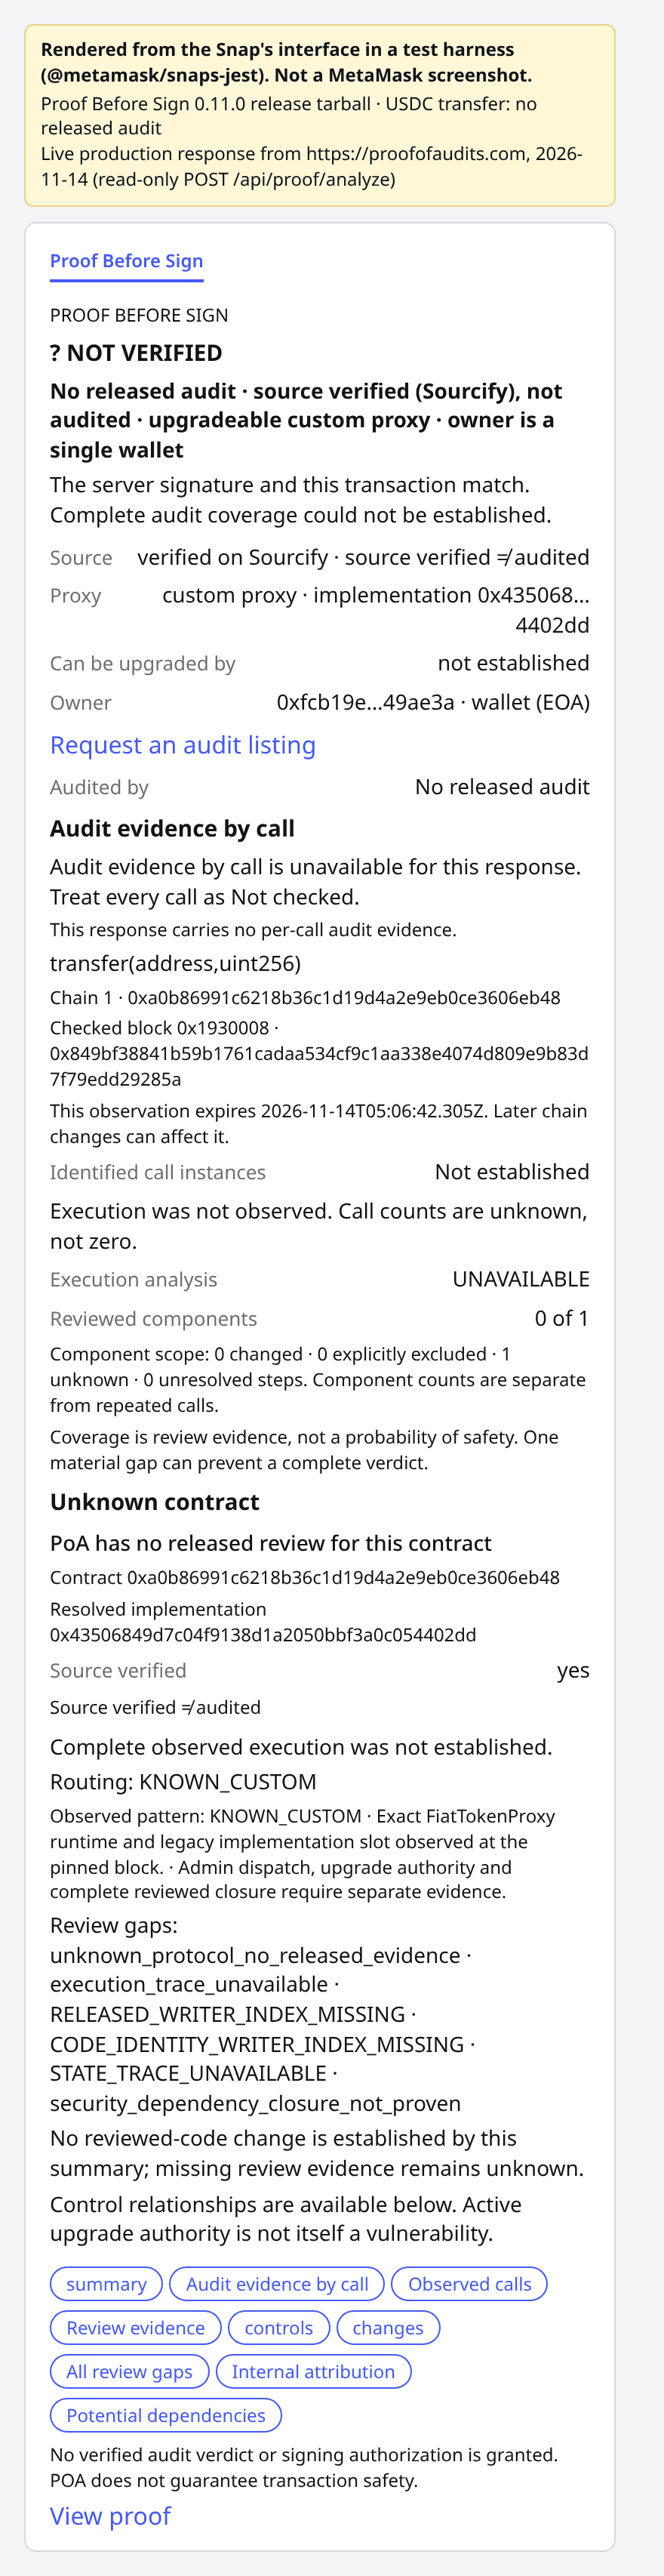
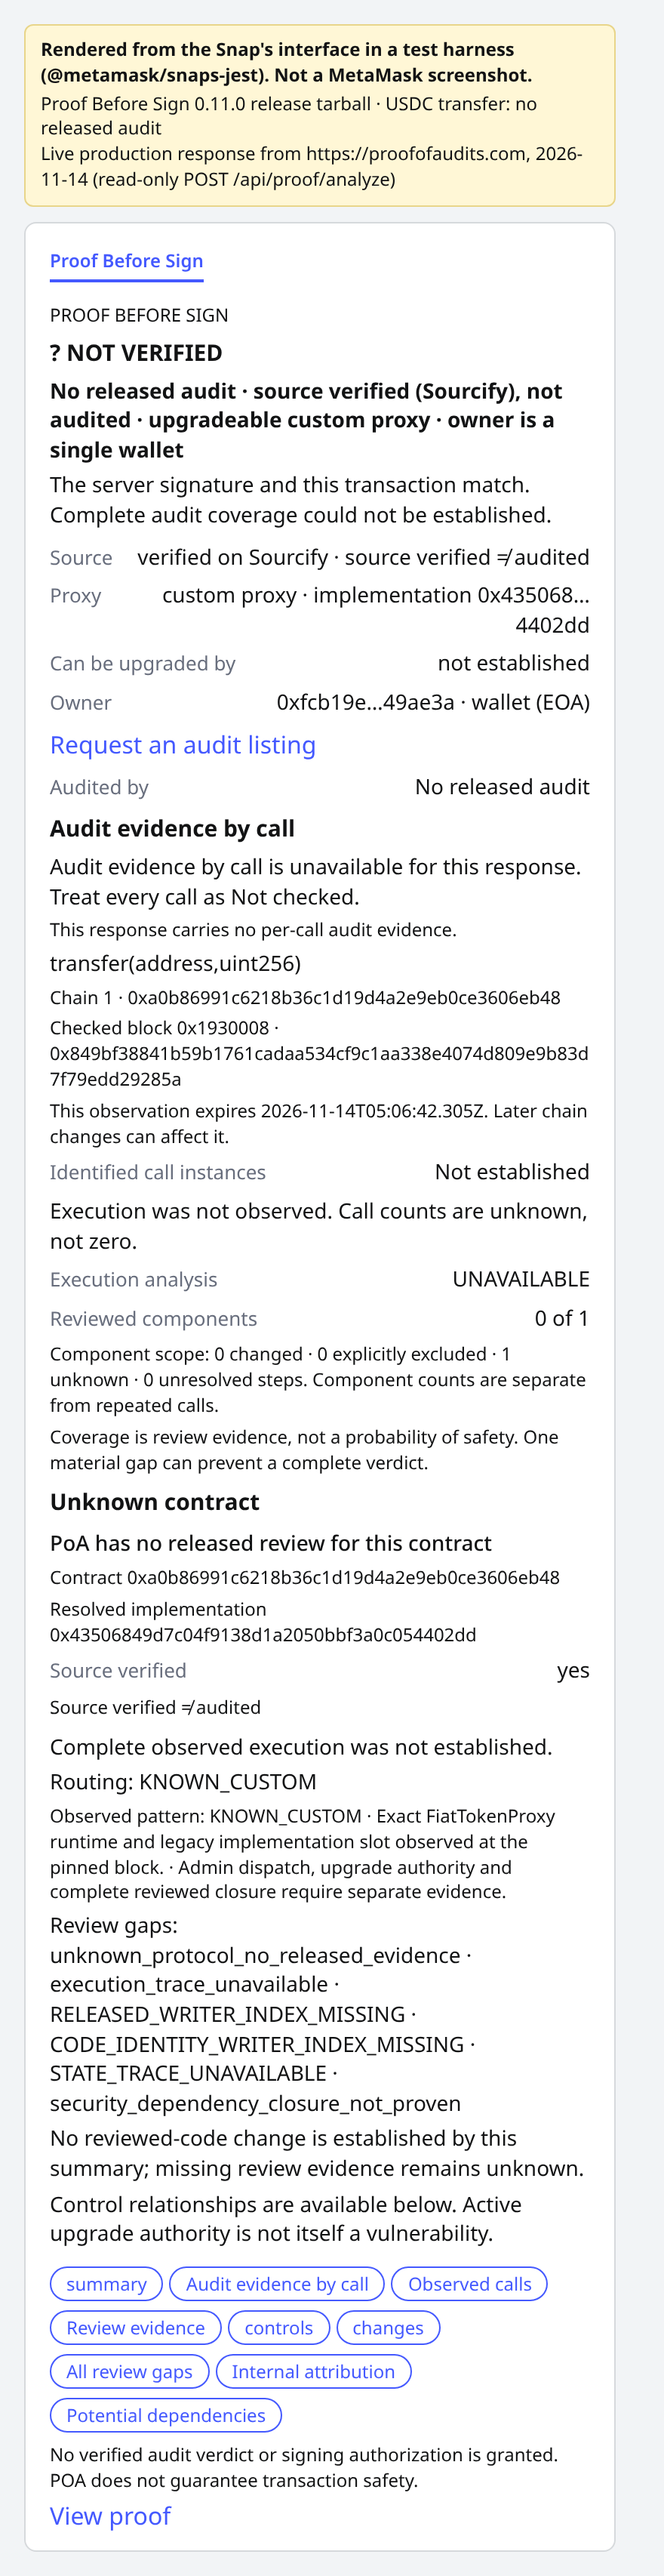
USDC transfer
No released audit, so the verdict is Not verified.
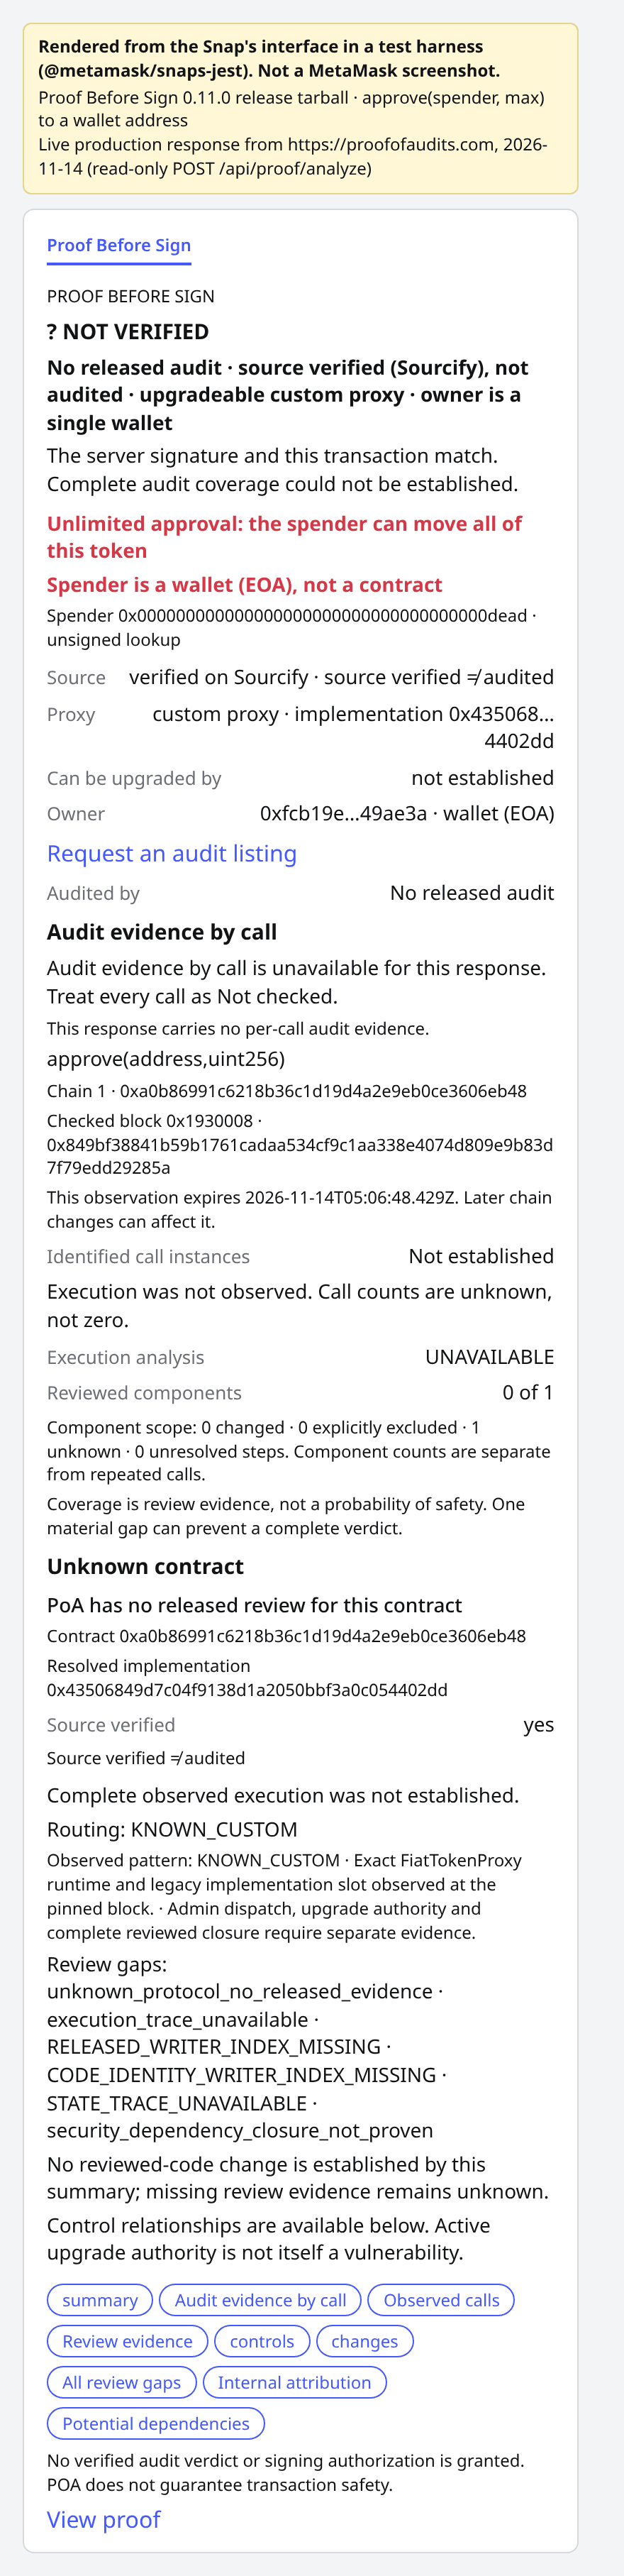
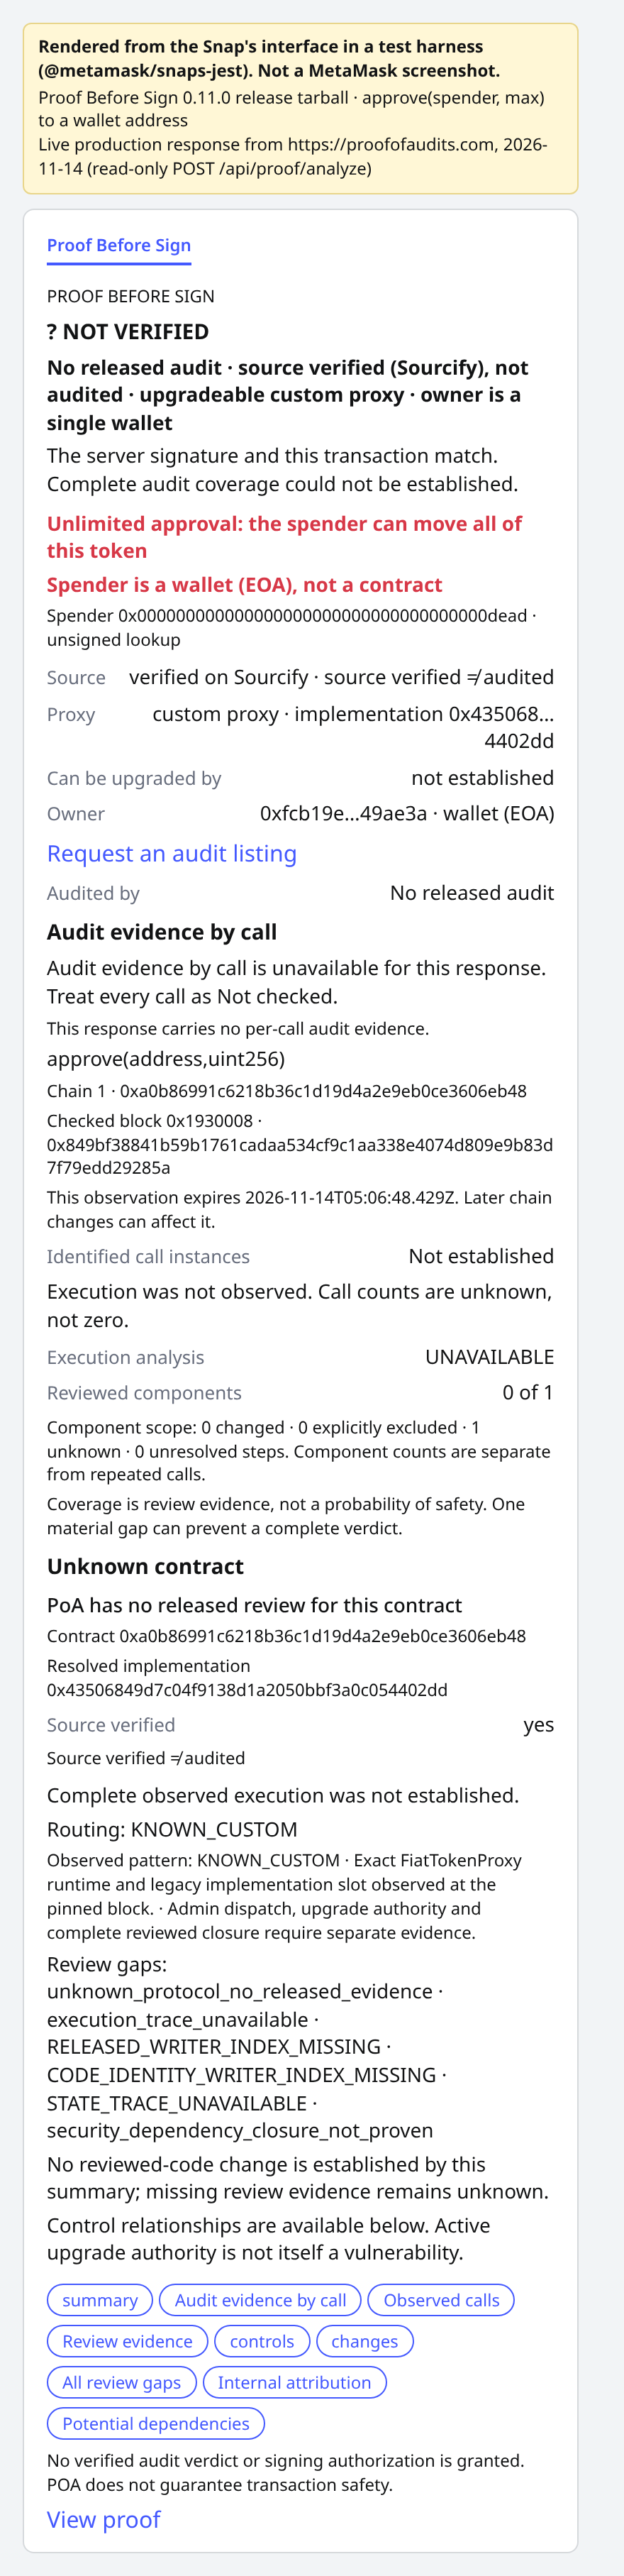
Unlimited approval
The spender is a wallet address, not a contract.
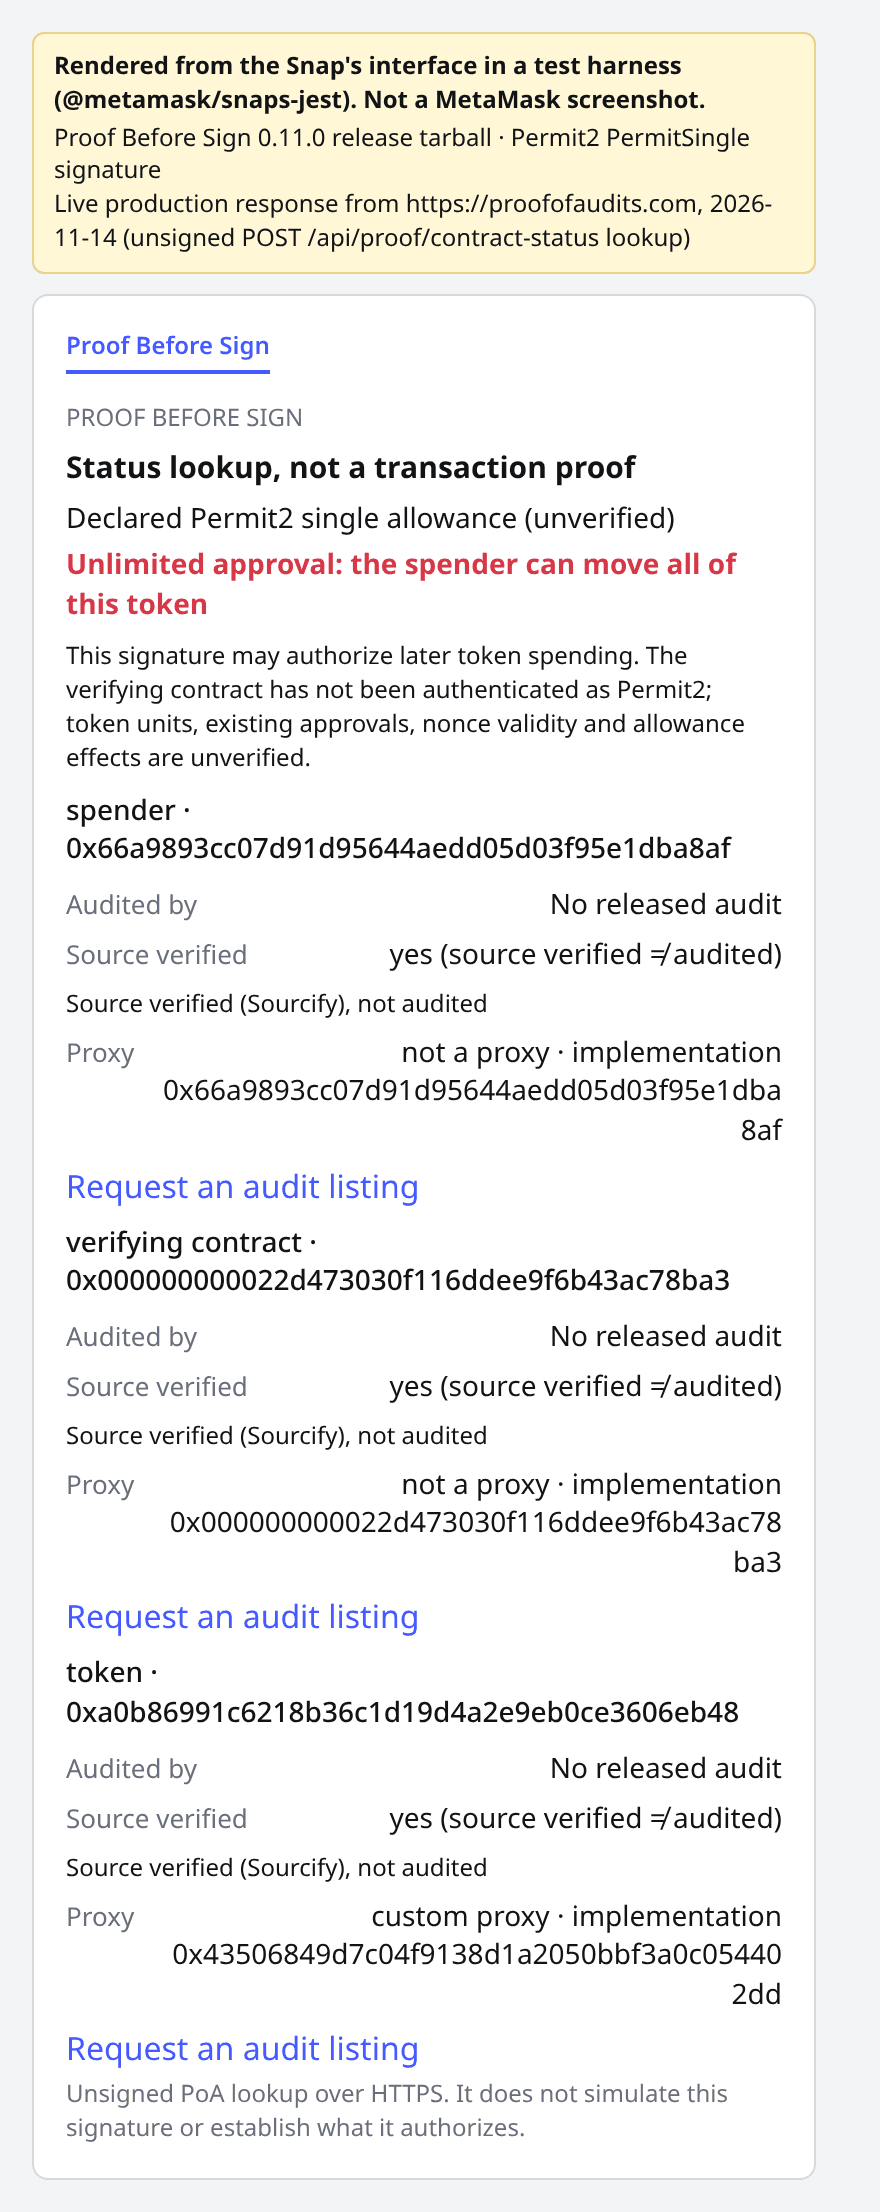
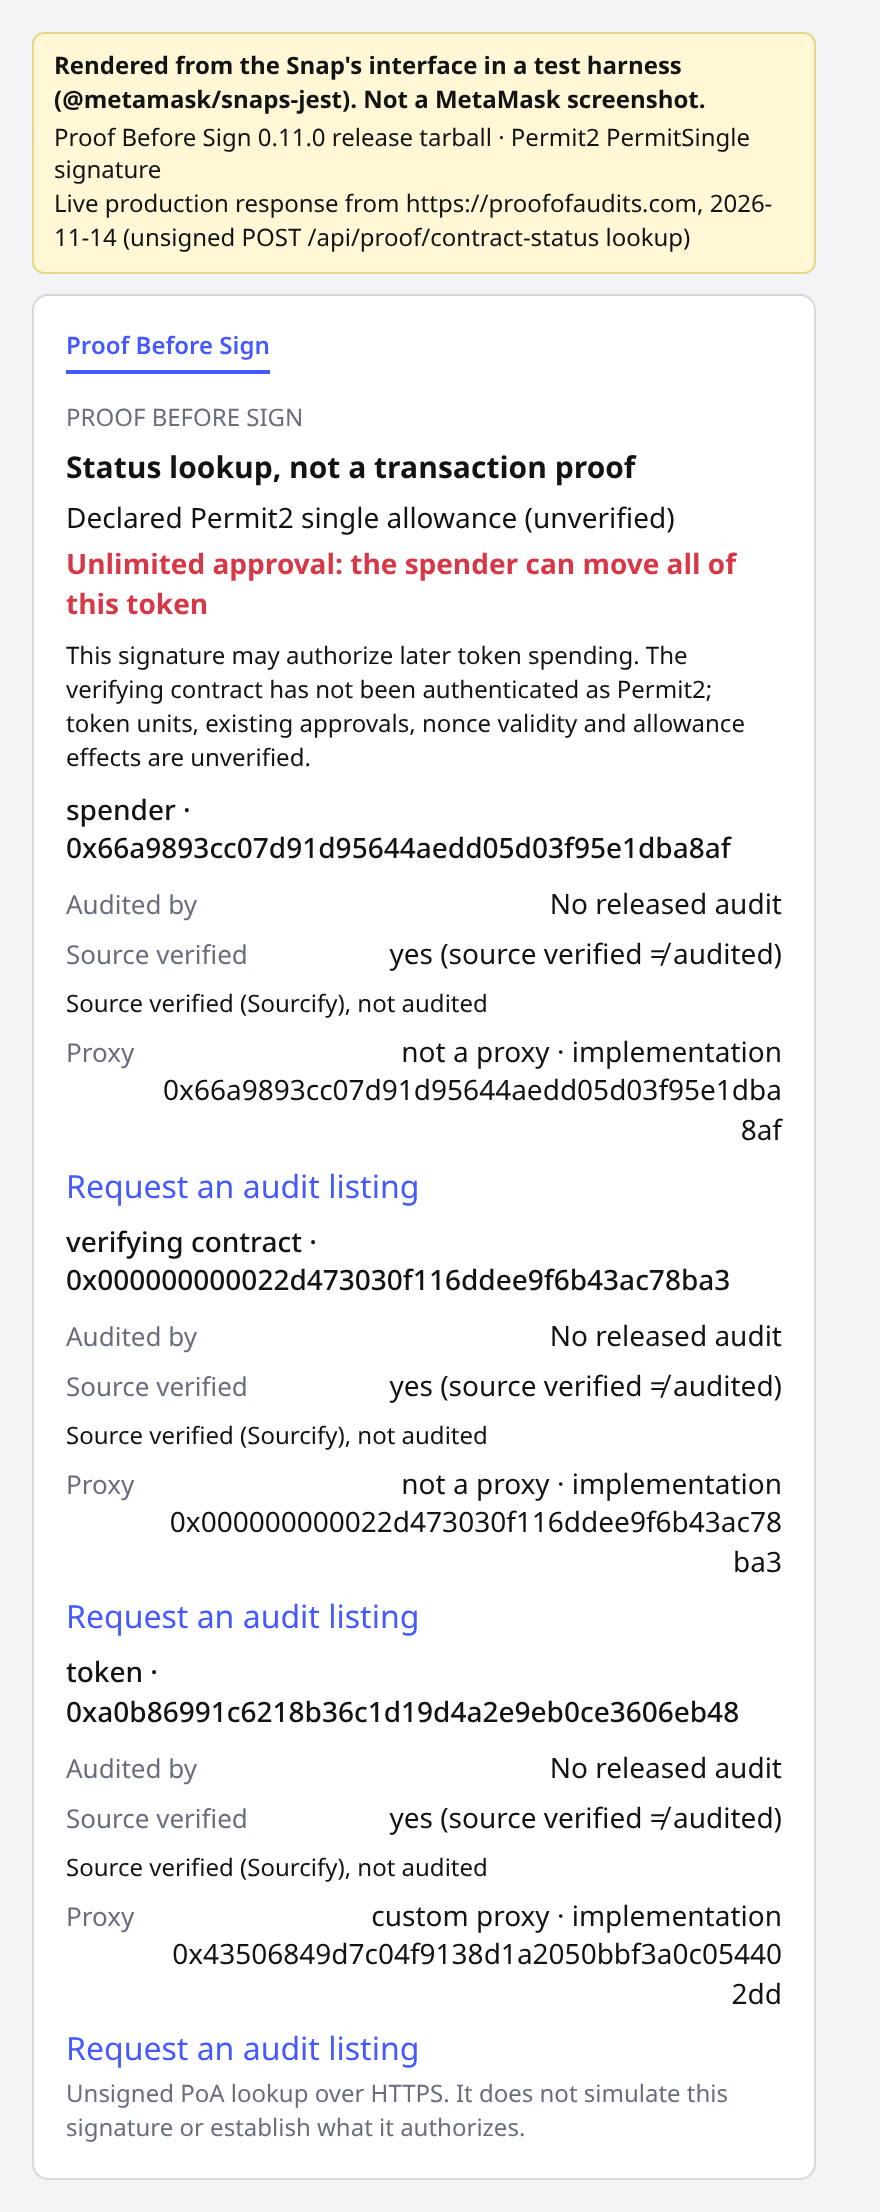
Permit2 signature
A status lookup for each contract the message names.
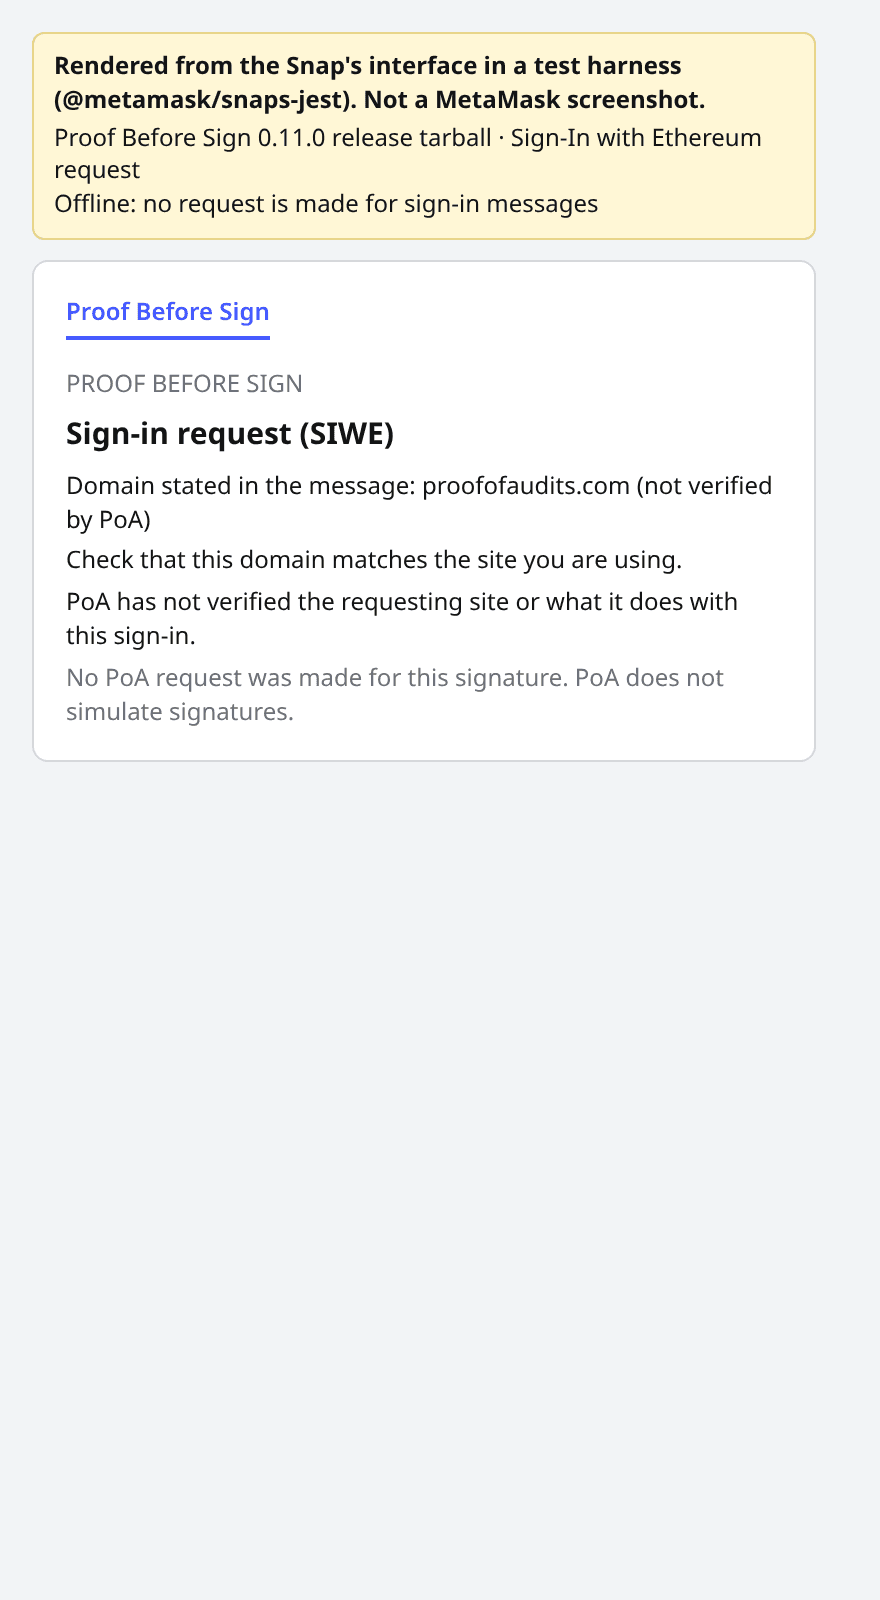
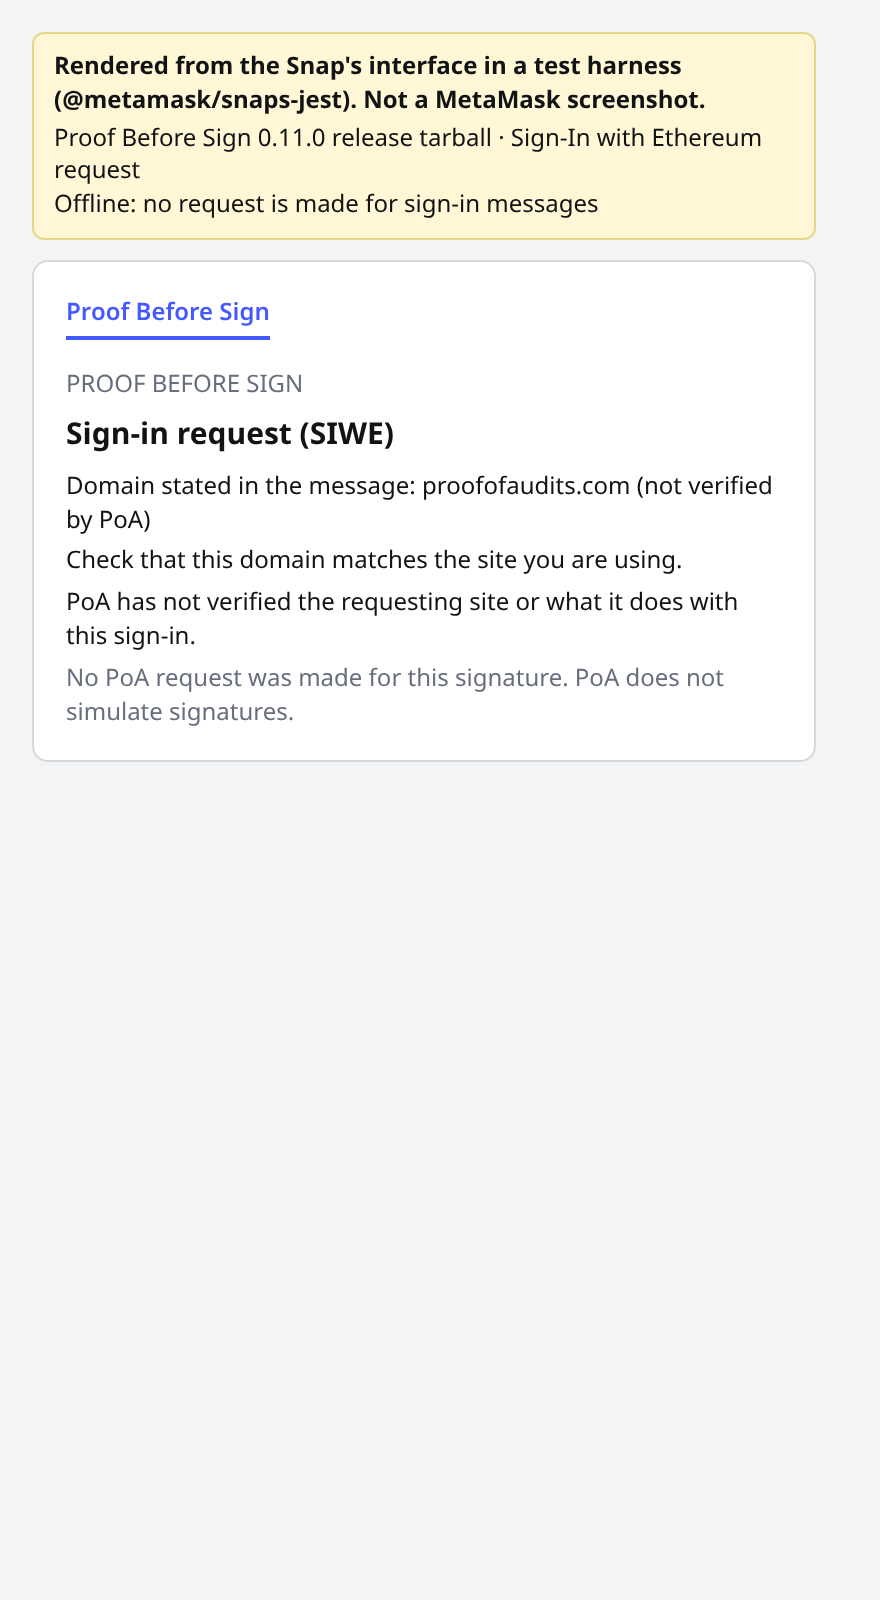
Sign-in with Ethereum
Offline: POA makes no request for sign-in messages.
Download
The release package
MetaMask installs the Snap from npm. You can download the same tarball and check it yourself.
- Package
- @proofofaudits/proof-before-sign-snap@0.11.0Release pending, not on npm yet
- Tarball
- proofofaudits-proof-before-sign-snap-0.11.0.tgz
- Size
- 87.3 KB (89,344 bytes)
- SHA-256
- decc0c9abfefae946566fbdf588338ca7dd34df3e7d2fc718eadba6bda6fe9c3
- Built
- 2026-11-14
- Source commit
- 5eb2a5bba6d5c130d7087eba286fa2d2acca3efd
Verify the tarball
Download the tarball npm serves and compare its SHA-256 with the value above. On Linux use sha256sum instead of shasum -a 256. The commands work once this version is published on npm.
curl -sL -o proofofaudits-proof-before-sign-snap-0.11.0.tgz https://registry.npmjs.org/@proofofaudits/proof-before-sign-snap/-/proof-before-sign-snap-0.11.0.tgz
shasum -a 256 proofofaudits-proof-before-sign-snap-0.11.0.tgz
MetaMask also checks the bundle against the checksum in the package's snap.manifest.json when it installs the Snap.
On a phone?
MetaMask Mobile does not support installing Snaps like this one. Open this page on a desktop computer in Chrome, Firefox, Brave, Edge or Opera with the MetaMask browser extension, then install from there.
How it works
- 01Install Proof Before Sign: in MetaMask Flask today, or in MetaMask once public installation opens. Approve the permissions MetaMask shows.
- 02Use a supported DeFi app as usual and start a contract transaction.
- 03POA traces each call in the order it runs, through proxies to their implementations. It checks every call against released review evidence and against public audit reports that name its file.
- 04The POA tab in MetaMask shows the verdict, then each call with its status and firms, findings on that path and who can change the code. “View proof →” opens the exact Passport.
Verdicts and call rows
What the Snap can tell you
Verdicts are computed by deterministic code from recorded evidence. AI research never approves coverage; evidence is released after independent PoA review, or by an approved audit firm with automated code checks.
The verdict
The verdict at the top of the panel counts released evidence only. It reads Verified only when released evidence covers the exact live code.
- VerifiedVERIFIED
- Released audit evidence covers the exact live code and the path this check needed.
- PartialPARTIAL
- Evidence covers part of this interaction. Something material is not covered.
- ChangedCHANGED
- Live code, path, configuration or control differs from what was reviewed.
- Not verifiedNOT VERIFIED
- No released evidence applies, or the facts needed could not be established. Not a finding of risk, and not a sign of safety.
The call rows
The rows under the verdict are evidence, not a release. A row reads In audit scope when a public audit report names the file that call runs; the deployed code has not been compared with the reviewed code. Only Byte-for-byte match means the deployed code is the build of the reviewed commit. No audit found and Not checked are not findings of risk. A call row never turns the verdict Verified.